
SecureChapter: the eCISO your security office never has to wake up.
The platform that unites governance, risk and compliance (GRC) with cyber operations in a single command layer. It tracks regulatory change, keeps your risk picture current, collects evidence as the work happens and walks you into every audit prepared.
Never sleeps · Never forgets · Never resigns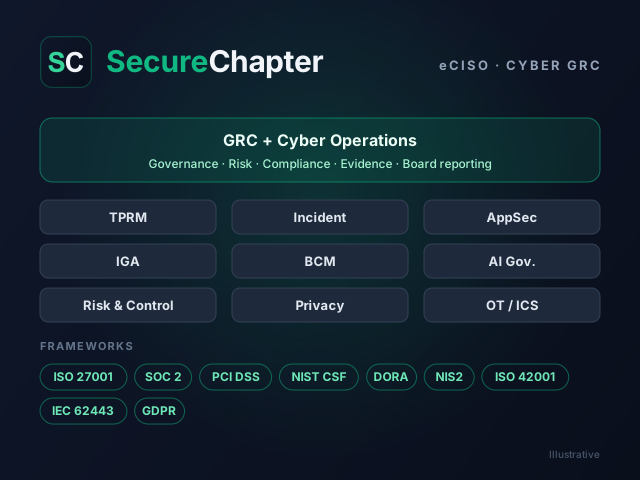
A security office that runs as software, with your own team at the helm.
No CISO yet? It builds the structure you are missing. Already have one? It gives your team leverage. It is not a chatbot or another scanner: it is the command layer where governance, risk, compliance and cyber operations meet.
What an eCISO is
- An always-on structure for governance, risk, compliance and cyber operations
- Institutional memory that outlives any single tenure
- Evidence collected as the work happens, not reconstructed at the last minute
- Board-ready answers on demand, with the evidence behind them
What an eCISO is not
- A chatbot making your security decisions
- A consultant on the clock
- Another scanner added to the pile
- A replacement for human judgement
What does your eCISO do every day?
The work a CISO office should do every day keeps running continuously, even when nobody is watching.
Watches the horizon
Regulations can change overnight: new deadlines, amendments, expectations. Your eCISO tracks what changed and what it means for you before it becomes an audit finding.
Keeps the risk picture current
Risks, vendors, assets, identities and exceptions in one living picture: where you stand today, not a spreadsheet that was true last quarter.
Collects the proof as you go
Evidence is gathered while the work happens, not dug up the weekend before an audit. Always current, always findable, always attributable.
Briefs the board
When leadership asks “Are we OK?”, your eCISO answers with posture, trends and the evidence behind them, in board language rather than engineer language.
Can you answer these questions today?
Answering them from spreadsheets takes weeks, if the answer exists at all. Your eCISO answers them with the evidence behind them.
- Which regulation changed overnight, and does it affect you?
- Which vendor could hurt you most tomorrow?
- Who, and which account, still has access it shouldn't?
- If the auditor arrived on Monday, how many weekends would it cost you?
- Can you prove your resilience, or only claim it?
- What does the board actually need on Thursday?
Switch on the modules you need today and expand as your risk landscape grows.
SecureChapter is not another scanner: it governs on top of the security tools you already run, turning their signals into oversight, evidence and decisions.
Third-Party Risk Management (TPRM)
Govern vendor risk across the full lifecycle, with a living risk profile for every vendor.
Cyber Incident Management
Run security incidents end to end, confidential by design.
Application Security
Keep application risks and exceptions under oversight.
Identity Governance & Administration (IGA)
Govern human and machine identities: review and certify access, and surface conflicts.
Business Continuity Management (BCM)
Plan, test and prove continuity.
AI Governance
Govern your use of AI before the regulators ask.
GRC: Risk & Control
The control core of the platform: risk register, controls and framework mapping.
Privacy & Data Protection
Turn your privacy obligations into day-to-day operations.
OT / ICS Security
Govern operational technology risk alongside IT.
Map controls once, report continuously against every framework.
Control mapping for KVKK (Turkish data protection law) and sector regulations (BDDK, SPK, SEDDK, etc.) is assessed together during the POC.
The eCISO meets you where you are.
Whether your CISO is on staff, you rent one, or you don't have the budget yet.
Growing companies
No CISO yet? CISO-grade structure from day one, ready for your first framework, your first audit and your biggest customer's security questionnaire.
Enterprises and their CISOs
You don't lack leadership, you lack leverage. One command layer over the tools you already run, and one evidence base for ISO 27001, SOC 2, NIS2 and DORA.
Holding groups and multi-entity organisations
Every subsidiary gets its own isolated eCISO at its own maturity; the group gets one consolidated posture. Acquisitions come under governance from the first week.
vCISOs, consulting and audit firms
Give every client an eCISO: portfolio view, strict client isolation, white-label reporting under your brand and one methodology.
Command centre, integrations and security
Executive & CISO Command Centre
- CISO dashboard with KRI tracking
- Board-ready report generation
- Regulatory attestation and evidence pack export
- Audit readiness score
- Role-based access with all standard roles predefined
Integrations
- SIEM / EDR connectors
- Cloud provider integrations
- CI/CD security pipeline hooks
- SSO / identity providers
- Evidence automation connectors
Secure by Design
- Post-quantum-ready, file-level encryption
- Defence in depth with extra hardening at the database layer
- Continuous penetration testing
- Multi-tenant architecture with strict tenant isolation
- Use as an internal tool or as white-labelled SaaS under your brand
Hire a CISO, rent a vCISO or gain an eCISO.
| Path | What it gives you | What to keep in mind |
|---|---|---|
| Hiring a CISO | The gold standard: dedicated, full-time leadership. | Hard to find, afford and keep; with short tenures, the search starts again. |
| Renting a vCISO | Senior expertise on tap. | Hours are finite, and knowledge often leaves with the engagement. |
| Gaining an eCISO | The standing layer underneath both: it works from day one, makes a CISO more effective and a vCISO more scalable. | It works best with a human at the helm: yours, or one you trust. |
Two ways: try it first, or buy directly.
In Türkiye you obtain SecureChapter through TurnCloudON: walkthrough, POC, quote and deployment with a single point of contact.
Proof of Concept (POC)
Start with a 30-minute live walkthrough and bring your hardest governance question. Then try the platform on your own scenarios with the frameworks and modules you choose. Scope, duration and success criteria are agreed in writing at the outset.
Direct Purchase
If your needs are clear, request a quote directly. Quote, contract and invoicing go through TurnCloudON; deployment, framework mapping and user support are provided by TurnCloudON experts.
Services alongside the platform
Our services that build, run and document the technical side of compliance can be combined end to end with SecureChapter.
KVKK, Law No. 5651 and ISO 27001 Compliance Support
Implementation and operation of the technical and administrative measures required by legislation, and production of audit-ready evidence.
Solution details →ISO 27001 Consulting
Setting up an information security management system, Annex A technical controls, evidence production and audit preparation.
View the service →KVKK Compliance Consulting
Implementation and operation of the technical and administrative measures required by Law No. 6698.
View the service →SecureChapter™ is a brand of ITC2 Services Ltd. (London, United Kingdom). TurnCloudON is SecureChapter's authorised reseller and strategic partner in Türkiye. Product information is compiled from the vendor's published materials and confirmed against the current scope at quotation.
Related guides
GRC Software
What is GRC (governance, risk and compliance) software, why move away from spreadsheets, and how does it help prepare for ISO 27001, NIS2 and DORA? POC with SecureChapter eCISO.
Read the guide →CISO, vCISO and eCISO
What is a CISO, when does a virtual CISO (vCISO) make sense, and what does an eCISO provide? Three ways to establish information security leadership, and SecureChapter eCISO.
Read the guide →A no-commitment start in three steps.
Discovery call
We spend 45 minutes understanding your environment and priorities. Free of charge.
Free initial assessment
After the meeting, a one-page note with initial findings and recommendations; the findings are yours to keep. A full health check and risk report are part of our accelerator packages.
Package or service
Start with an accelerator package or go straight to managed services.